LMS single sign-on through your own identity provider
Connect an OpenID Connect identity provider such as Microsoft Entra ID, Okta or Google Workspace, so staff and members sign in with the account they already have. Add two-factor by role for anyone who still uses a password. SAML 2.0 is not supported.
Your identity provider handles the password and any multi-factor prompt. Continuum creates or matches the learner account when they arrive.
- Accounts created on first sign-in
- Password sign-in can be switched off
- Two-factor by role for password logins
What is LMS single sign-on?
LMS single sign-on (SSO) lets people open their training with the account they already use at work, instead of keeping a separate username and password for the LMS. In Continuum Learn, each team connects one OpenID Connect (OIDC) identity provider, and learners get a sign-in button on the login page that sends them to that provider.
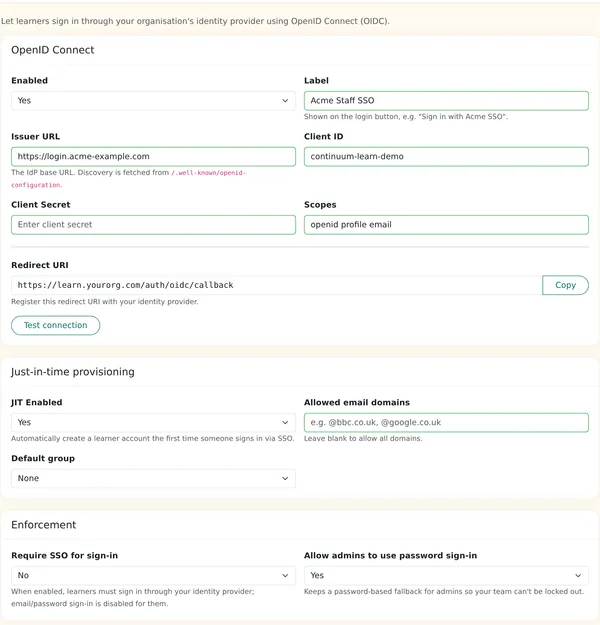
You enter the provider's issuer URL, a client ID and secret, and register the redirect address Continuum shows you. A Test connection button checks that the provider's discovery document can be read before you save. Turn on just-in-time provisioning and a learner account is created the first time someone signs in, optionally limited to certain email domains and placed in a default group. Turn on Require SSO and password sign-in is switched off for learners, with an option to keep a password fallback for admins so nobody is locked out.
What is supported? Continuum supports OpenID Connect with provider discovery, and one provider per team. Microsoft Entra ID, Okta and Google Workspace all offer OIDC, but your application set-up still needs checking with a full sign-in test. SAML 2.0 is not supported, so a provider that can only issue SAML applications, such as ADFS or Shibboleth without OIDC, cannot connect today.
Sign-in is only one part of access control. For the rest, see member training LMS for membership bodies, white-label LMS for putting the sign-in page on your own web address, and all features.
Learners use your provider's sign-in button, with accounts created on first sign-in when you turn it on
See it in the product
Screens from Continuum Learn. The provider details shown are made-up examples.
Connect your provider
Enter the issuer URL, client ID and secret, copy the redirect address into your provider, and test the connection.
Two-factor policy by role
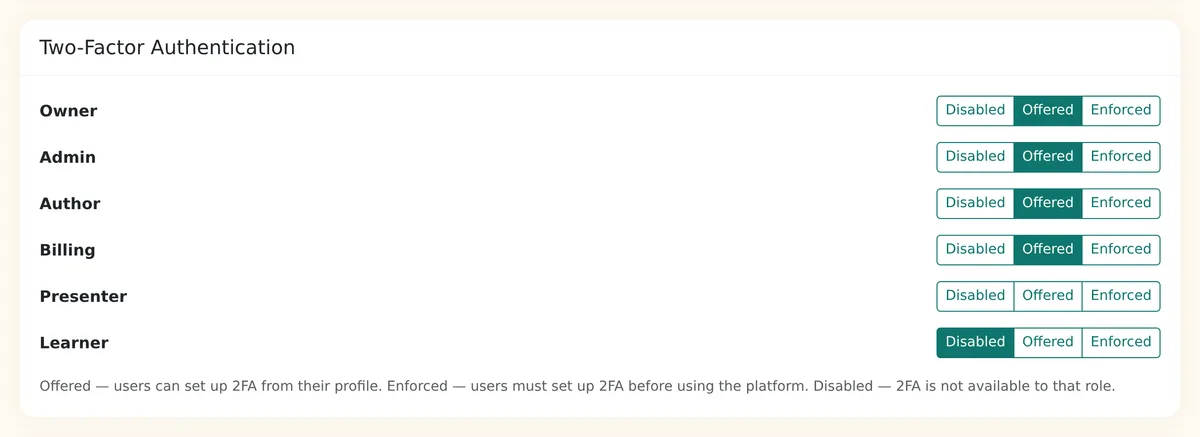
Each role can be Disabled, Offered or Enforced. Enforced users must set up an authenticator app before they can use the platform.
Why connect your LMS to your identity provider
Fewer passwords for learners to remember, with sign-in managed through your identity provider.
One account for everything
Learners sign in with the credentials they use for the rest of work. No separate LMS password to remember or reset.
No manual account set-up
With just-in-time provisioning, a learner account is created on first sign-in and can be placed in a default group straight away.
Enforce it when you are ready
Switch on Require SSO and learners can no longer sign in with a password. Admins can keep a password fallback so you cannot lock yourselves out.
Two-factor where passwords remain
Choose Disabled, Offered or Enforced per role, so owners, admins and authors can be required to use an authenticator app.
Who uses single sign-on with their LMS
Employers with a managed directory
Let staff sign in through your organisation's OpenID Connect provider, and control which new accounts can be created automatically.
Membership bodies
Members reach training from the member area without a second login. For sites that sign members in themselves, there is a separate signed-link sign-in for external membership integrations. See embed courses on your website.
Teams that need stronger admin security
Require an authenticator code for owners, admins and authors while leaving learners on simple sign-in.
SSO and two-factor features in Continuum Learn
Everything below is in the product today
OpenID Connect sign-in
Authorisation code flow with state, nonce and PKCE, and the provider discovered from its standard well-known address.
Test connection
Check that the issuer's discovery document can be read, and see its endpoints, before you save and enable the provider.
Login button with your label
The login page shows a sign-in button with the label you choose, such as Sign in with Acme SSO.
Just-in-time provisioning
Create learner accounts on first sign-in and optionally add them to a default group. An email-domain list controls automatic account creation, with exceptions for pre-approved email addresses.
Require SSO
Turn off password sign-in for learners, including password reset, with an option to keep a password fallback for admins.
Careful account linking
An existing account is linked automatically only if it was never claimed and belongs to this team alone. Otherwise the person confirms with their existing password first.
Authenticator-app two-factor
Learners scan a QR code with a standard authenticator app, and get eight one-time recovery codes in case they lose the device.
Two-factor policy per role
Set Disabled, Offered or Enforced separately for owner, admin, author, billing, presenter and learner. A person with several roles gets the strictest.
Sessions tied to the team
A session created by SSO is only valid on that team's addresses, and a super-admin account cannot be used through a team's SSO.
Frequently asked questions
Does Continuum Learn support SAML?
No. Continuum supports OpenID Connect only. If your identity provider can only issue SAML applications, it cannot be connected today. Most current providers, including Microsoft Entra ID, Okta and Google Workspace, also offer OIDC, so check whether you can create an OIDC application there.
Which identity providers work with the LMS?
Continuum connects through OpenID Connect. Microsoft Entra ID, Okta and Google Workspace all offer it. The Test connection button checks the provider's discovery document; run a complete sign-in test before you require SSO.
Can learners be created automatically when they first sign in?
Yes. Turn on just-in-time provisioning and a learner account is created the first time someone signs in through your provider. You can limit it to certain email domains and add new accounts to a default group. Leave the domain list blank to allow every domain.
Can we stop people signing in with a password?
Yes. Switch on Require SSO and learners must sign in through your provider, including when they try to reset a password. You can keep password sign-in available for admins, which is the default, so a provider outage or a mistake in the set-up does not lock your team out.
Can we enforce two-factor authentication for admins?
Yes. In Manage settings, set each role to Disabled, Offered or Enforced. Enforced roles must set up an authenticator app before they can use the Manage and Create areas, and they get recovery codes. The code is requested on password sign-in. People who sign in through SSO rely on the multi-factor rules in your own identity provider.
What happens if someone already has an account with the same email?
It depends on the account. If it was never claimed and belongs to this team alone, it is linked automatically. Otherwise the person is asked to enter their existing password once to confirm the link, and two-factor users must also enter their code. Super-admin accounts cannot be used through a team's SSO.
Can members sign in from our own membership website?
Yes, through a separate signed-link sign-in built for external membership integrations such as a WordPress member area. It is configured separately from OpenID Connect. See embed courses on your website for the options.
Does it use our own web address?
Yes. SSO works with a team that uses its own domain, and the sign-in completes safely on the platform before returning to your address. See white-label LMS.
Does disabling someone in our identity provider remove their LMS access straight away?
No. Disabling the account in your provider stops future sign-ins, but it does not end a session that is already open in Continuum or remove the learner's enrolments. Remove the learner from your team in Continuum as part of your leavers process.
Check your identity provider will connect
Book a demo and tell us which provider you use. We will confirm it supports OpenID Connect and show you the set-up on a live team.